
Cybersecurity threats are becoming increasingly sophisticated, making application security a major priority for businesses and software development teams. As organizations rely on websites, mobile applications, and cloud-based software, vulnerabilities in source code can expose sensitive information and create opportunities for cyberattacks. Identifying these weaknesses before applications are released is an important part of secure software development.
This is where Static Application Security Testing (SAST) becomes valuable. SAST helps developers identify potential security vulnerabilities by examining application code without executing the software. Understanding what SAST is in cyber security, how it works, and how it differs from other security testing methods can help organizations build safer applications and strengthen their overall cybersecurity strategies.
What Is SAST in Cyber Security?
SAST stands for Static Application Security Testing, a cybersecurity testing method that examines application source code, bytecode, or other supported program representations to identify potential security weaknesses. Unlike testing approaches that require applications to run, SAST analyzes software without executing it. This makes it particularly useful during the early stages of software development, when developers can address vulnerabilities before deployment.
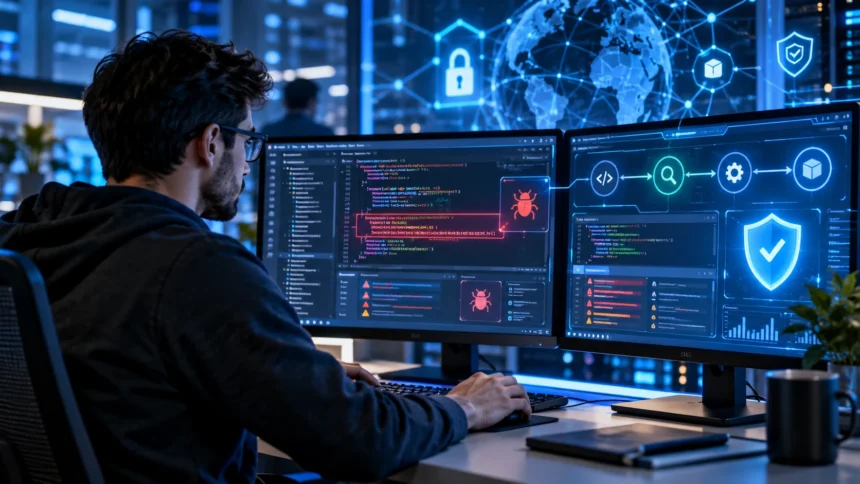
Static application security testing tools analyze code structures, programming patterns, and potential data flows to identify suspicious behavior. Depending on the tool and programming language, SAST may detect insecure coding practices, unsafe input handling, or potentially dangerous application functions. The results help developers investigate security concerns and determine whether corrective changes are necessary.
SAST is commonly associated with white-box security testing because it uses information about an application’s internal code. Development teams can integrate these tools into existing workflows to review security during coding and testing. Although SAST cannot detect every vulnerability, it provides valuable insight into code-level weaknesses that might otherwise remain unnoticed until later development stages.
How Does Static Application Security Testing Work?
Static Application Security Testing works by examining the internal structure of application code and identifying patterns associated with security vulnerabilities. The process typically begins when a developer submits code for analysis or an automated development pipeline launches a security scan. The testing tool evaluates supported files using analysis rules and techniques designed to identify potentially unsafe programming behavior.
Advanced SAST tools may use control-flow analysis, data-flow analysis, and taint analysis to understand how information moves through an application. For example, a tool may trace untrusted user input toward a database query and check whether appropriate safeguards are present. This helps identify possible injection vulnerabilities before the application is executed.
After analyzing the code, the tool generates findings that may include vulnerability descriptions, affected file locations, and suggested remediation steps. Developers review these results to distinguish genuine security risks from incorrect warnings. Once relevant issues are corrected, the application can be scanned again to verify whether the identified code-level weaknesses have been addressed.
What Types of Vulnerabilities Can SAST Detect?
SAST tools can identify various security weaknesses, depending on their analysis capabilities, supported programming languages, and configured detection rules. Common examples include potential SQL injection, cross-site scripting, command injection, and path traversal vulnerabilities. These problems often occur when applications process untrusted information without appropriate validation, encoding, or other protective measures.
Some SAST solutions also identify insecure cryptographic practices, unsafe function usage, and certain memory management problems. For example, an analyzer may flag code that uses outdated cryptographic algorithms or passes untrusted input to dangerous system functions. Tools supporting languages such as C and C++ may additionally detect selected memory safety weaknesses.
However, discovering suspicious code does not automatically confirm that an attacker can exploit it. Some findings represent genuine vulnerabilities, while others depend on application context or protective measures the analyzer cannot recognize. Security teams should investigate results carefully and combine static analysis with other testing methods to develop a more complete understanding of application security.
Why Is SAST Important for Application Security?
SAST is important because it helps developers identify security problems before vulnerable code reaches production environments. Addressing weaknesses during development is often less disruptive than responding after a public application has been compromised. Early detection also gives engineering teams more opportunities to understand the causes of insecure coding practices and prevent similar mistakes.
Another advantage is improved visibility into security risks across large software projects. Development teams may work with thousands of files, complex frameworks, and frequent code changes that make manual security reviews difficult. Automated static code analysis helps identify potential problems consistently, allowing security specialists to focus on findings that require deeper investigation.
SAST also supports a proactive approach to cybersecurity by making code security part of normal development activities. Instead of treating security assessments as isolated events before release, organizations can review changes throughout the software development lifecycle. This approach strengthens collaboration between developers and security professionals while encouraging greater responsibility for secure application design.
SAST vs. DAST: What Is the Difference?
SAST and DAST are two important application security testing methods, but they examine software from different perspectives. SAST analyzes internal application code without running the program, while Dynamic Application Security Testing (DAST) examines a running application. DAST typically interacts with exposed application interfaces to identify security weaknesses that become observable during execution.
One major advantage of SAST is that it can identify potential vulnerabilities early in development and often point developers toward specific code locations. DAST, meanwhile, can evaluate application behavior in a deployed or testing environment. It may identify weaknesses related to authentication, exposed functionality, and certain runtime security configurations.
Neither testing method provides complete coverage of all cybersecurity threats. SAST may miss issues that depend on runtime behavior, while DAST may struggle to identify vulnerabilities in code paths it cannot reach. Combining static and dynamic security testing can provide a broader assessment of application risks than depending on either approach alone.
SAST vs. SCA and IAST in Cybersecurity
SAST is frequently compared with Software Composition Analysis (SCA), although these tools address different security concerns. SAST primarily examines application code for potential programming vulnerabilities, while SCA identifies third-party libraries and software dependencies. SCA tools can help organizations recognize components with known vulnerabilities, outdated versions, or licensing considerations that require attention.
Interactive Application Security Testing (IAST) offers another approach by analyzing application behavior during execution using instrumentation or other supported observation techniques. Unlike SAST, which examines code without running it, IAST uses information collected while the application operates. Its effectiveness depends on factors such as application compatibility, test coverage, and the capabilities of the chosen solution.
Modern application security programs often combine SAST, SCA, DAST, and other specialized testing tools. Each method contributes different information about vulnerabilities, dependencies, and application behavior. Using complementary approaches helps security teams investigate risks more effectively and reduces the likelihood of relying on incomplete results from a single testing technique.
How SAST Supports DevSecOps and Secure Development
DevSecOps integrates security practices into software development and operations workflows rather than treating cybersecurity as a separate final-stage activity. SAST supports this approach by allowing developers to identify code-level weaknesses during regular development. Integrating security analysis into established engineering processes can help teams address vulnerabilities without repeatedly interrupting development schedules.
Many organizations incorporate SAST scanning into continuous integration and continuous delivery pipelines. When developers submit code changes, automated checks can analyze the affected application and report potential security issues. Teams may configure policies for reviewing high-risk findings before changes are merged or released, depending on their security requirements.
This approach is often described as shifting security left because important security checks occur earlier in the development lifecycle. However, early testing should complement rather than replace monitoring, runtime protection, and production security assessments. A mature DevSecOps strategy combines automated analysis, developer education, secure design practices, and ongoing evaluation of deployed applications.
How to Implement SAST Testing Step by Step
The first step in implementing SAST is identifying which applications, programming languages, and development environments require security analysis. Organizations should evaluate existing coding practices, security requirements, and available resources before selecting a testing solution. Understanding these factors helps teams choose tools that support their technology stack and produce findings relevant to actual risks.
Next, configure the selected SAST tool and run an initial scan to establish a security baseline. Review the findings, investigate potentially serious vulnerabilities, and prioritize remediation according to exploitability, business impact, and available evidence. Developers should understand why identified code patterns may be unsafe instead of making superficial changes merely to silence warnings.
After addressing initial weaknesses, integrate automated scanning into regular development workflows. Configure appropriate scan frequency, reporting responsibilities, and procedures for handling new findings. Repeated testing, documented remediation decisions, and periodic reviews can help organizations maintain stronger application security as new features, dependencies, and code changes are introduced.
How to Choose the Best SAST Tools
Selecting a suitable SAST tool depends on the programming languages, frameworks, project size, and security objectives of the organization. Some solutions provide broad language coverage and centralized reporting, while others specialize in particular development environments. The most useful tool is one that accurately identifies relevant security risks and fits existing engineering practices.
Popular SAST-related solutions include <Entity category=”software” value=”Semgrep” disambig=”static code analysis and security scanning platform”/>, <Entity category=”software” value=”Checkmarx” disambig=”application security testing platform”/>, and <Entity category=”software” value=”SonarQube” disambig=”code quality and security analysis platform”/>. These products differ in their analysis capabilities, deployment options, integrations, and licensing models. Organizations should evaluate supported security features carefully because general code quality analysis does not always provide the same depth as dedicated application security testing.
Important selection criteria include scanning speed, finding accuracy, developer experience, integration capabilities, and reporting quality. Teams should also consider whether tools support custom security rules, automated workflows, and appropriate access controls. Testing shortlisted solutions against representative applications can provide a more reliable basis for selection than comparing marketing claims or feature lists alone.
What Are the Benefits of SAST in Cybersecurity?
One of the main benefits of SAST is earlier identification of potential security vulnerabilities during software development. Developers can investigate and correct problematic code before applications are released to users. This reduces dependence on late-stage security reviews and can help organizations avoid some of the operational costs associated with fixing vulnerabilities after deployment.
Another advantage is the ability to perform automated security checks across repeated code changes. SAST tools can support consistent analysis, making it easier to identify newly introduced coding risks. When results include accurate code locations and useful explanations, developers can spend less time searching for problems and more time implementing appropriate fixes.
Static security testing can also support organizational security standards and secure coding initiatives. Reports provide evidence of performed checks and help teams monitor remediation progress over time. Although scanning alone does not establish regulatory compliance, documented security testing can contribute to broader application security governance, risk management, and software quality improvement efforts.
What Are the Limitations and Challenges of SAST?
Despite its advantages, SAST has limitations that organizations must understand before relying on its findings. One common challenge is false positives, where analysis tools identify suspicious code that does not represent an exploitable vulnerability. Large numbers of inaccurate warnings can overwhelm development teams and reduce confidence in automated security testing.
False negatives present another challenge because some vulnerabilities may not be detected by the configured analyzer. Runtime configuration problems, complex business logic weaknesses, and certain authentication flaws can be difficult to identify through static analysis alone. Language compatibility, incomplete build information, and unsupported frameworks may further restrict the effectiveness of specific tools.
Implementing SAST also requires time for configuration, developer training, finding review, and remediation. Organizations that scan every project without establishing clear priorities may create unnecessary workloads and slow development. A balanced approach focuses on meaningful risks, appropriate automation, and complementary testing methods rather than expecting static analysis to solve every security problem.
Best Practices for Effective SAST Security Testing
Effective SAST testing begins with clear security ownership and realistic implementation goals. Development teams should define how findings are classified, investigated, corrected, and documented. Prioritizing vulnerabilities according to severity and application context helps ensure that significant security risks receive attention without overwhelming engineers with lower-priority warnings.
Regular scanning is particularly valuable when applications undergo frequent changes or receive contributions from multiple developers. Teams should integrate SAST into appropriate development workflows and maintain updated rules for supported technologies. Reviewing recurring vulnerabilities can also reveal coding patterns that should be addressed through training, reusable secure components, or improved development standards.
Artificial intelligence may increasingly assist static analysis by explaining findings, suggesting potential fixes, and helping developers review complex code. However, automatically generated recommendations can introduce mistakes or overlook important security context. Human verification, secure coding knowledge, and responsible handling of proprietary source code remain essential for maintaining trustworthy application security testing.
Conclusion
Understanding what SAST is in cyber security is essential for developers and organizations seeking to improve software protection. Static Application Security Testing examines application code to identify potential vulnerabilities before execution. By integrating SAST into development workflows, teams can detect insecure coding practices earlier and reduce their exposure to preventable application security risks.
SAST provides important benefits, including automated analysis, developer-friendly findings, and stronger support for secure software development. However, false positives, incomplete detection coverage, and runtime blind spots mean it should not be treated as a complete security solution. Combining SAST with DAST, SCA, and other appropriate testing methods helps create broader cybersecurity coverage.
As software systems become more complex, reliable application security testing will remain important for protecting sensitive information and maintaining user trust. Organizations should choose suitable tools, establish practical remediation processes, and encourage secure development habits. A balanced strategy that combines automated testing with human expertise provides a stronger foundation for long-term application security.
Frequently Asked Questions (FAQs)
1. What Is the Full Form of SAST in Cyber Security?
SAST stands for Static Application Security Testing. It is a cybersecurity testing method that analyzes source code or other supported program representations without executing the application to identify potential security vulnerabilities.
2. What Is the Main Purpose of SAST Testing?
The main purpose of SAST is to identify security weaknesses during software development. It helps developers discover potentially insecure coding practices early and correct vulnerabilities before applications reach production environments.
3. What Is the Difference Between SAST and DAST?
SAST examines application code without executing the program, while DAST tests a running application. Both approaches identify different categories of security concerns and can complement each other.
4. Can SAST Detect All Security Vulnerabilities?
No, SAST cannot identify every security vulnerability. It may miss runtime configuration issues, complex business logic problems, and certain application behavior weaknesses, making additional security testing necessary.
5. Is SAST Important for DevSecOps?
Yes, SAST supports DevSecOps by integrating automated code security analysis into development workflows and CI/CD pipelines. It helps teams detect vulnerabilities earlier, maintain secure coding practices, and improve application security.