
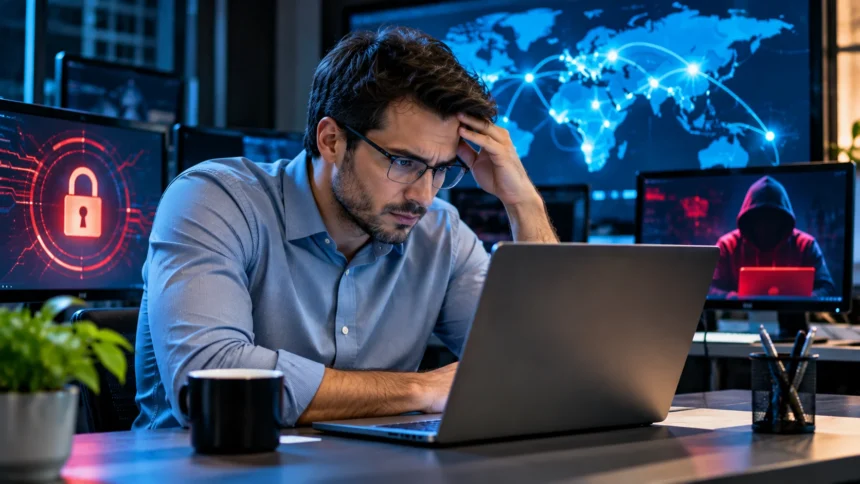
Cybersecurity risks are a growing concern for businesses, organizations, and individuals who rely on digital technology. Every online account, connected device, and digital application can introduce potential security weaknesses. From data breaches to financial fraud, cyber threats can affect personal information, business operations, and customer trust. Understanding these risks is an important step toward creating a safer digital environment.
Modern cybersecurity involves more than protecting computers from viruses. Businesses must also consider phishing attacks, cloud vulnerabilities, insider threats, identity theft, and third-party security weaknesses. As organizations adopt more digital tools, their exposure to potential security incidents can increase. However, not every threat presents the same level of danger.
Learning about cybersecurity risks helps people recognize common threats and understand how security measures reduce potential damage. This guide explains major types of cybersecurity risks, their possible consequences, and practical ways to manage them. It also explores how organizations can assess security weaknesses, protect sensitive information, and improve their overall digital resilience.
What Are Cybersecurity Risks?
Cybersecurity risks refer to the possibility that digital threats or security weaknesses could cause harm to an individual or organization. These risks may involve unauthorized access, stolen information, disrupted services, or financial losses. They arise when vulnerabilities, valuable digital assets, and potential threats interact within a technology environment.
A cybersecurity threat is not exactly the same as a cybersecurity risk. A threat is something that could cause harm, such as malicious software or an unauthorized access attempt. Risk considers both the likelihood of that threat causing an incident and the potential consequences. This distinction helps organizations evaluate security concerns more effectively.
Cybersecurity risks exist across computers, mobile devices, cloud applications, business networks, and connected equipment. Their importance depends on the information and services involved. For example, unauthorized access to a sensitive customer database could create serious consequences. Understanding these differences helps organizations prioritize protection according to actual business needs.
Why Cybersecurity Risks Matter More Than Ever
Businesses increasingly depend on digital technology for everyday communication, financial transactions, customer service, and operational management. This dependence creates significant benefits, but it also introduces potential security exposure. A disruption affecting one important system may interrupt several connected business processes and prevent employees from completing essential tasks.
Cloud platforms, mobile applications, and remote work arrangements have expanded the number of systems organizations need to protect. Sensitive information may travel between employees, external providers, and online services. Without appropriate controls, these connections can increase opportunities for unauthorized access or accidental information exposure.
Cybersecurity risks also extend beyond immediate technical damage. A serious incident may affect customer confidence, regulatory obligations, operational costs, and business relationships. Some consequences continue long after systems have been restored. Understanding the wider impact helps decision-makers recognize why cybersecurity should remain part of regular business planning.
Phishing and Social Engineering Risks
Phishing is one of the most familiar cybersecurity risks because it relies on deceptive communication rather than complicated technical methods. Attackers may send fraudulent emails, text messages, or other messages that appear to come from trusted organizations. Their objective may be to obtain confidential information, compromise accounts, or encourage unauthorized actions.
Social engineering involves manipulating people into making decisions that weaken security. For example, a fraudulent message might impersonate a company representative and request sensitive documents. Other attacks may create unnecessary urgency to discourage careful verification. These methods demonstrate how human judgment can become an important part of digital security.
Organizations can reduce these risks through employee awareness, email protection, and reliable identity verification procedures. Staff should know how to question unexpected requests and report suspicious communication. Phishing-resistant multi-factor authentication can provide additional account protection. However, technical safeguards and training work best when supported by clear workplace policies.
Malware and Ransomware Risks
Malware is malicious software designed to interfere with computers, applications, or information. Different types of malware may steal sensitive records, damage files, or provide unauthorized access to systems. Malware infections can affect individual devices or become part of larger incidents involving business networks and essential digital services.
Ransomware presents a particularly serious risk because it can prevent organizations from accessing important information and disrupt normal operations. Some ransomware incidents also involve data theft or threats to expose confidential records. The consequences may include service interruptions, recovery expenses, privacy concerns, and significant financial uncertainty.
Reducing malware exposure requires several protective measures working together. Regular software updates, endpoint protection, restricted permissions, and secure system configurations help limit opportunities for compromise. Organizations should also maintain protected backups and test recovery procedures. No single security product guarantees protection against every form of malicious software.
Data Breaches and Information Theft
A data breach occurs when information is accessed, disclosed, or exposed without appropriate authorization. Personal details, financial records, business documents, and customer information may all be affected. Breaches can result from external attacks, internal mistakes, poorly configured systems, or weaknesses involving third-party providers.
The consequences depend on the sensitivity of the information and how it is misused. Exposed customer details may create privacy concerns, while stolen business records can affect competitive interests or contractual obligations. Organizations may also face investigation costs, legal responsibilities, and reputational damage after a serious incident.
Data protection requires understanding where sensitive information is stored and who can access it. Encryption, appropriate permissions, secure storage, and data retention policies can reduce exposure. Businesses should also avoid collecting unnecessary personal information. Protecting data throughout its lifecycle helps reduce the potential consequences of unauthorized disclosure.
Weak Passwords and Account Takeover Risks
Weak authentication is a significant cybersecurity risk because online accounts often provide access to confidential information and valuable services. Reused passwords can be especially dangerous when credentials are exposed through a separate incident. An attacker who obtains valid login information may attempt to access additional accounts that use the same credentials.
Account takeover can affect email services, business applications, financial platforms, and administrative systems. Compromised accounts may allow unauthorized actions or expose sensitive information. Privileged accounts deserve particular attention because they may control important settings and multiple connected services. The potential consequences extend beyond the affected login.
Strong account security begins with unique credentials and appropriate authentication methods. Password managers can help people maintain different passwords where necessary. Passkeys and phishing-resistant multi-factor authentication can provide additional protection when available. Organizations should also disable unnecessary accounts and regularly review access permissions.
Cloud Security and Misconfiguration Risks
Cloud services allow organizations to store information, run applications, and access computing resources without managing every physical server themselves. However, cloud adoption introduces responsibilities involving permissions, configuration, and data protection. A poorly configured cloud service may expose information or provide access beyond what the organization intended.
One common risk involves granting users or applications excessive permissions. Another concerns storage services that become accessible to unintended audiences because of incorrect settings. Cloud environments can also contain forgotten resources that no longer receive appropriate monitoring. These weaknesses may remain unnoticed without accurate inventories and regular assessments.
Cloud security requires understanding the responsibilities shared between the provider and the customer. Organizations should review access controls, monitor important resources, and assess configuration settings. Automated security tools can help identify certain problems. However, their findings still require appropriate evaluation and maintenance by knowledgeable personnel.
Insider Threats and Employee-Related Risks
Insider threats involve security risks associated with people who have authorized access to an organization’s systems or information. Employees, contractors, and other trusted users may create problems through accidental mistakes or deliberate misuse. Not every insider-related incident involves malicious intentions, making this category especially important for practical risk management.
Unintentional incidents may involve sending confidential information to the wrong recipient, misplacing a device, or using an unauthorized application. Deliberate misuse can involve inappropriate access or disclosure of sensitive records. The consequences depend on the user’s permissions and the importance of the affected information.
Organizations can reduce insider-related risks through clear access policies, employee education, and appropriate monitoring. Limiting permissions to necessary responsibilities helps reduce unnecessary exposure. Businesses should also provide simple reporting procedures for mistakes. A constructive security culture encourages early reporting rather than making employees afraid to disclose problems.
Third-Party and Supply Chain Cybersecurity Risks
Many businesses depend on external technology providers, software vendors, cloud services, and support contractors. These relationships can improve efficiency but may also introduce cybersecurity risks. A security incident affecting a supplier may disrupt services or expose information belonging to several connected organizations.
Third-party exposure can be difficult to manage because businesses do not always control their suppliers’ internal security practices. A vendor may handle sensitive records, maintain software components, or access business systems remotely. If those connections are insufficiently protected, problems outside the organization may affect its own operations.
Vendor risk management helps businesses understand these dependencies. Organizations can assess supplier security practices, review contractual protections, and restrict unnecessary access. Maintaining alternative service arrangements may also improve resilience where practical. Regular supplier reviews help ensure that changing business relationships do not create overlooked security weaknesses.
Remote Work and Mobile Device Security Risks
Remote work allows employees to access company resources from different locations, creating flexibility for many organizations. However, laptops, smartphones, and home networks introduce additional security considerations. Devices may contain confidential files or provide access to sensitive applications, making their protection important even outside traditional office environments.
Lost devices, outdated software, and insecure account access can increase exposure to security incidents. Personal devices may create additional challenges when business information is stored alongside private content. Organizations need policies that address these situations without unnecessarily interfering with employees’ personal information or normal activities.
Device encryption, strong authentication, security updates, and appropriate endpoint management can reduce risks. Businesses should also establish procedures for reporting missing devices and suspicious activity. Employees benefit from clear instructions about approved applications and information sharing. Effective remote work security balances protection with practical access to business resources.
Financial, Legal, and Reputational Cybersecurity Risks
Cybersecurity incidents can create financial consequences through disrupted operations, technical recovery, legal assistance, and other response expenses. Some organizations may also experience lost revenue when essential services become unavailable. The total financial impact depends on the incident’s severity, the affected systems, and the organization’s ability to recover.
Legal consequences may arise when compromised information falls under privacy, consumer protection, or industry-specific requirements. Organizations may need to assess whether notification or other obligations apply. These requirements vary by jurisdiction and circumstances. Appropriate legal guidance can be important when an incident involves sensitive personal information.
Reputational harm is another risk because customers and business partners expect organizations to protect information responsibly. A serious incident can weaken trust, particularly when communication is unclear or recovery is delayed. Transparent responses and meaningful corrective actions may help rebuild confidence. However, reputational outcomes depend on the organization’s conduct and the nature of the incident.
How to Assess and Prioritize Cybersecurity Risks
Cybersecurity risk assessment helps organizations identify threats, understand vulnerabilities, and evaluate potential consequences. The process generally begins with identifying important digital assets such as customer databases, financial systems, and essential applications. Understanding these resources makes it easier to determine which security problems deserve the greatest attention.
Risk evaluation often considers the likelihood of a harmful event and the severity of its potential impact. A vulnerability affecting a critical public-facing service may deserve more urgent attention than an issue involving an isolated, low-impact system. However, simple risk scores should not replace professional judgment or relevant technical evidence.
Businesses can document their findings in a risk register that records identified concerns, responsible owners, and planned responses. Regular reviews help keep this information relevant as systems change. Prioritizing risks allows organizations to direct limited resources toward meaningful improvements instead of treating every possible threat as equally urgent.
Best Practices for Reducing Cybersecurity Risks
Reducing cybersecurity risks requires a combination of prevention, detection, response, and recovery measures. Strong authentication, regular software updates, and restricted access provide a useful foundation. Network monitoring and endpoint security tools can help identify suspicious activity. However, these measures must be configured and maintained appropriately to remain effective.
Employee education is equally important because many security incidents involve everyday decisions and communication. Training should explain how to recognize suspicious requests, protect sensitive information, and report potential problems. Clear guidance is usually more useful than overwhelming employees with technical terminology. A supportive reporting culture can help organizations identify risks earlier.
Businesses should also maintain reliable backups and documented incident response procedures. Testing recovery processes helps determine whether essential services can be restored after a disruption. Regular security assessments provide opportunities to identify overlooked weaknesses. Continuous improvement is more effective than assuming cybersecurity protection is complete after an initial investment.
Common Mistakes When Managing Cybersecurity Risks
One common mistake is assuming that installing antivirus software eliminates cybersecurity threats. Antivirus products address certain risks, but they cannot replace access controls, employee awareness, backups, and secure system configurations. A narrow approach may leave important weaknesses unaddressed while creating a false sense of security.
Another mistake is ignoring less visible risks, including excessive permissions, outdated software, and supplier dependencies. These problems may not interrupt daily operations immediately, making them easier to overlook. However, they can contribute to serious incidents when combined with other weaknesses. Routine reviews help organizations identify problems before they become more disruptive.
Businesses may also focus heavily on preventing incidents while neglecting response and recovery planning. Even strong defenses cannot guarantee that every attack will fail. Without clear procedures, a security incident may create unnecessary confusion and prolonged downtime. Effective risk management prepares organizations to respond when preventive measures are insufficient.
Conclusion
Cybersecurity risks affect nearly every area of modern digital activity. Phishing, ransomware, data breaches, account compromise, and cloud security weaknesses can create significant problems for individuals and organizations. Understanding how these threats operate helps identify where protective measures are most important and why different risks require different responses.
Managing cybersecurity risks involves more than purchasing advanced security tools. Businesses need clear policies, informed employees, strong authentication, regular software maintenance, and reliable recovery procedures. Assessing risks according to their likelihood and potential impact can improve decision-making. A layered security approach helps reduce dependence on any single protective measure.
Ultimately, cybersecurity is an ongoing responsibility rather than a one-time project. Technology, business activities, and security threats continue to change, making regular reviews essential. By understanding common risks and applying appropriate safeguards, organizations can protect important information, improve operational resilience, and maintain greater confidence in their digital systems.
Frequently Asked Questions
What Are the Most Common Cybersecurity Risks?
Common cybersecurity risks include phishing, malware, ransomware, data breaches, weak passwords, cloud misconfigurations, insider threats, and third-party vulnerabilities. Their potential impact depends on the affected systems, available safeguards, and information involved.
What Is the Difference Between a Cybersecurity Risk and a Threat?
A cybersecurity threat is something that could cause digital harm, such as malicious software. Cybersecurity risk considers the likelihood of that threat causing an incident and the consequences that could follow.
How Can Small Businesses Reduce Cybersecurity Risks?
Small businesses can reduce risks through multi-factor authentication, regular software updates, employee training, secure backups, and appropriate access controls. Prioritizing essential systems and common threats helps make limited security resources more effective.
Why Are Data Breaches a Serious Cybersecurity Risk?
Data breaches can expose personal information, financial records, and confidential business documents. Their consequences may include privacy violations, recovery expenses, legal obligations, operational disruption, and reduced customer confidence.
How Often Should Organizations Assess Cybersecurity Risks?
Organizations should review cybersecurity risks regularly and after significant changes involving technology, operations, or suppliers. The appropriate frequency depends on business complexity, regulatory requirements, and the importance of affected systems.