
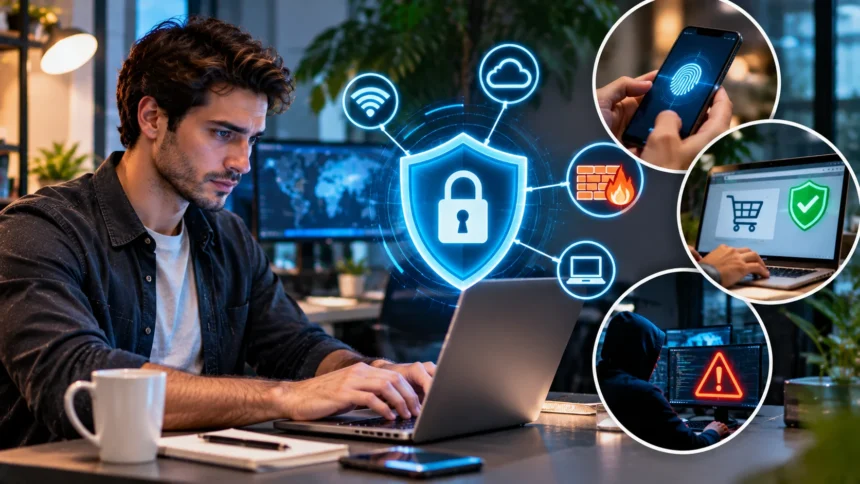
Cybersecurity works by protecting computers, networks, applications, and digital information from unauthorized access, attacks, and damage. Every time you sign in to an account, send a message, or make an online payment, different security technologies may work together to protect your information. These protections help identify suspicious activity, control access, and reduce the possibility of cyber threats.
Understanding how cybersecurity works can help individuals and businesses make safer decisions online. From passwords and firewalls to encryption and malware detection, cybersecurity uses several methods to protect digital systems. This guide explains the main cybersecurity processes with clear examples, practical applications, and simple explanations of the technologies used to maintain digital security.
What Is Cybersecurity and How Does It Work?
Cybersecurity is the practice of protecting computers, networks, devices, and digital information against unauthorized activities. It combines security technologies, organizational policies, and responsible user behavior to reduce digital risks. Rather than depending on one protective tool, cybersecurity uses multiple layers of defense. Each layer addresses different threats and helps limit damage if another protective measure fails.
For example, imagine someone trying to access an online banking account without permission. A strong password creates an initial barrier, while multi-factor authentication provides additional verification. Security monitoring may also identify unusual login activity. These protections work together to make unauthorized access more difficult and help the service respond to suspicious behavior.
Cybersecurity also involves detecting problems, responding to incidents, and restoring affected systems. Security teams review unusual activity, investigate possible threats, and take appropriate corrective action. Regular software updates and reliable backups support ongoing protection. This continuous approach is necessary because attackers, technologies, and potential vulnerabilities change over time.
The Three Main Principles of Cybersecurity
Cybersecurity commonly follows three fundamental principles known as confidentiality, integrity, and availability. These principles are often called the CIA triad and provide a foundation for information security planning. Each addresses a different aspect of protecting digital information. Together, they help organizations evaluate whether their systems are secure, reliable, and accessible to authorized users.
Confidentiality means that sensitive information should be available only to people with appropriate permission. For example, a hospital must restrict access to patient records so unauthorized individuals cannot view private medical details. Passwords, encryption, and access controls help support confidentiality. These measures protect information during storage, transmission, and everyday use.
Integrity ensures that information remains accurate and is not changed without authorization. Availability means that authorized users can access systems and information when needed. For example, an online store must protect order details from unauthorized changes while keeping its website accessible to customers. Effective cybersecurity considers all three principles rather than focusing exclusively on preventing data theft.
How Firewalls Protect Computers and Networks
A firewall is a security system that monitors and controls network traffic according to established rules. It helps determine which connections should be permitted or blocked. Firewalls may operate on individual computers, network devices, or cloud platforms. Their primary purpose is to reduce unwanted communication between protected systems and potentially untrusted networks.
For example, a business firewall may prevent unauthorized external connections from reaching internal office systems. It can allow approved services while blocking traffic that violates security policies. This helps reduce opportunities for unauthorized access. However, firewalls cannot identify every malicious activity, particularly when harmful communication appears similar to legitimate traffic.
Modern firewalls may offer additional capabilities, including application awareness and intrusion prevention features. Security administrators configure these tools according to organizational requirements and regularly review their performance. Incorrect settings can accidentally block legitimate activity or leave unnecessary access available. Firewalls work best when combined with secure software, authentication, and continuous network monitoring.
How Antivirus Software Detects Malware
Antivirus software helps identify, block, and remove certain forms of malicious software from computers and other devices. Malware includes viruses, worms, spyware, ransomware, and other programs designed to perform harmful activities. Security software examines files, applications, and system behavior for suspicious characteristics. Detection methods vary according to the product and the threats being investigated.
For example, someone might receive an unexpected email attachment containing harmful software. An antivirus program may recognize the file as dangerous and quarantine it before it runs. Other security tools monitor application behavior to identify suspicious activities that are not associated with known malware signatures. These capabilities provide additional protection against different types of threats.
However, antivirus protection is not a guarantee against every infection. New malicious programs, deceptive downloads, and software vulnerabilities can sometimes bypass detection. Keeping security software updated improves its ability to recognize emerging threats. Users should also avoid suspicious attachments, install trusted applications, and maintain current operating system updates.
How Passwords and Authentication Keep Accounts Safe
Authentication is the process of verifying that someone attempting to access a system is authorized to do so. Passwords remain a common authentication method for websites, applications, and online accounts. A strong, unique password helps reduce the risk of unauthorized access. However, passwords can sometimes be stolen through phishing, data breaches, or other security incidents.
Multi-factor authentication adds another layer of protection by requiring more than one form of verification. For example, a user may enter a password and then confirm their identity through an authenticator application or security key. This additional requirement can prevent unauthorized access when a password becomes compromised. Some modern authentication systems also support passkeys.
A password manager can help users create and store different passwords for multiple accounts. This reduces the temptation to reuse familiar credentials across websites. Users should also protect account recovery methods and avoid sharing verification codes. Strong authentication combines suitable technology with careful account management rather than relying on password complexity alone.
How Encryption Protects Sensitive Information
Encryption protects information by transforming readable data into a format that cannot be understood without the appropriate decryption key. It is commonly used when information travels across networks or remains stored on devices. Encryption helps protect confidentiality if data is intercepted or accessed without authorization. However, its effectiveness depends on secure implementation and proper key management.
For example, when someone connects to a legitimate website using HTTPS, encryption helps protect information exchanged between the browser and the website. This reduces the ability of outsiders to read transmitted passwords or payment details. However, HTTPS does not guarantee that the website itself is trustworthy. Fraudulent websites can also use encrypted connections.
Encryption also protects information stored on laptops, smartphones, and business servers. Full-disk encryption can help prevent someone from reading stored files if a locked device is lost or stolen. Organizations may additionally encrypt sensitive databases and backups. These protections should be combined with authentication and access controls because encryption cannot prevent every form of unauthorized access.
How Cybersecurity Detects Phishing Attacks
Phishing is a deceptive communication technique used to obtain sensitive information or persuade people to perform unsafe actions. Attackers may impersonate banks, delivery companies, employers, or familiar online services. Messages often contain urgent requests involving passwords, payments, or account verification. Cybersecurity systems attempt to identify these messages before they cause harm.
Email security tools examine sender information, message content, links, and attachments for suspicious characteristics. For example, an email filter may flag a message that imitates a bank while directing users to an unrelated website. Some systems also analyze patterns associated with previously identified phishing campaigns. However, sophisticated messages may still avoid automated detection.
Users provide an important additional layer of protection by verifying unexpected requests independently. Instead of following an unfamiliar link, they can visit the organization’s official website through a trusted method. Employees should also have clear procedures for reporting suspicious messages. Combining technical filtering with awareness training helps reduce phishing-related security incidents.
How Network Security Monitoring Identifies Threats
Network security monitoring involves observing activity across connected systems to identify unusual behavior and potential threats. Organizations collect information from network devices, servers, applications, and security tools. Analysts examine this information for signs of unauthorized access or suspicious communication. Monitoring helps organizations recognize problems that preventive controls may not have stopped.
For example, a security system might notice repeated unsuccessful login attempts against an employee account. It could also identify an unexpected increase in information leaving a company server. These activities may indicate a possible security problem, although legitimate explanations are sometimes possible. Security analysts investigate the surrounding evidence before determining whether an incident occurred.
Security information and event management systems, commonly called SIEM platforms, can help organize and analyze large volumes of security records. They connect information from multiple sources and generate alerts based on defined rules or detected patterns. However, excessive alerts can overwhelm analysts. Effective monitoring requires appropriate configurations, prioritization, and regular improvements to detection procedures.
How Cloud Cybersecurity Protects Online Data
Cloud cybersecurity protects information, applications, and services hosted through cloud computing platforms. Businesses often use cloud services to store documents, operate websites, and support remote collaboration. These systems require suitable security controls because information may be accessed from different locations and devices. Protection involves both cloud providers and their customers.
For example, a company storing documents in a cloud platform can limit access to authorized employees. Authentication, encryption, activity logging, and permission settings help protect the files. Cloud providers generally secure parts of the underlying infrastructure, while customers remain responsible for certain configurations and data management decisions. The exact division depends on the service.
Incorrect cloud settings can expose information even when the provider maintains strong infrastructure security. Publicly accessible storage, excessive account permissions, and unused credentials may create unnecessary risks. Organizations should regularly review configurations and remove access that is no longer required. Cloud security depends on understanding shared responsibilities and maintaining appropriate controls throughout the service lifecycle.
How Cybersecurity Works in Online Banking
Online banking illustrates how different cybersecurity methods protect sensitive financial activities. Banks commonly use authentication, encryption, transaction monitoring, and access restrictions to protect customer accounts. These measures help prevent unauthorized access and identify potentially suspicious activity. Financial institutions may also use additional verification procedures for transactions involving unusual circumstances.
For example, a banking system might notice a transaction that differs significantly from a customer’s usual behavior. Automated monitoring may flag the activity for additional verification or review. However, unusual transactions are not always fraudulent, so systems must consider the possibility of false alarms. Human investigators may help resolve cases requiring more detailed examination.
Customers can support banking security by protecting account credentials and reviewing transaction notifications. They should verify unexpected messages and contact the institution through established channels when something appears suspicious. Using secure devices and enabling suitable authentication options provides additional protection. Effective banking cybersecurity combines institutional safeguards with responsible customer practices.
How Businesses Respond to Cybersecurity Incidents
Cybersecurity incident response is the organized process used when a suspected or confirmed security problem occurs. Organizations generally begin by identifying the incident and assessing its potential impact. They then take appropriate steps to contain the problem and protect affected systems. A documented response plan helps teams coordinate their responsibilities during stressful situations.
For example, if ransomware affects a company computer, security personnel may isolate the device to reduce possible spread. They investigate which systems are affected and determine how the incident occurred. Recovery may involve restoring clean backups and correcting the vulnerabilities that contributed to the problem. The exact response depends on the incident and organizational circumstances.
After recovering, businesses should review what happened and identify improvements for future prevention. This may include updating security controls, improving employee training, or changing response procedures. Relevant legal or contractual notification requirements must also be considered. Incident response is not simply about restoring technology; it also supports accountability, learning, and operational resilience.
How Software Updates and Backups Improve Security
Software updates are important because developers regularly discover and correct vulnerabilities in operating systems, browsers, and applications. Attackers may exploit known weaknesses when security patches have not been installed. Applying relevant updates helps reduce exposure to these problems. However, updates should be obtained through trusted sources and managed appropriately in business environments.
For example, a company may discover that an outdated application contains a security vulnerability. Installing the approved update can remove or reduce the weakness before it is exploited. Organizations may use centralized tools to track which devices require attention. Regular maintenance helps prevent outdated software from becoming an avoidable entry point for cyber threats.
Backups provide protection when information becomes unavailable because of accidental deletion, system failure, or malicious activity. A reliable backup strategy includes protected copies and regular restoration testing. Some backups should be isolated from ordinary systems to reduce the risk of simultaneous compromise. Together, updates and backups support both cybersecurity prevention and recovery.
How Artificial Intelligence Supports Cybersecurity
Artificial intelligence and machine learning can help cybersecurity teams examine large amounts of information and identify potentially suspicious patterns. These technologies are useful when security systems generate more data than analysts can review manually. Models may help classify events, prioritize alerts, or recognize unusual activity. However, their findings require appropriate validation and oversight.
For example, a machine learning system may identify a sudden change in account activity that differs from established behavior. It can flag the event for investigation without automatically concluding that an attack occurred. This supports faster prioritization when numerous alerts need attention. The model’s usefulness depends on reliable data and appropriate evaluation.
AI-based security tools also have limitations because attackers can adapt their behavior and legitimate activities sometimes resemble threats. Incorrect alerts may waste time, while missed detections can create security risks. Organizations should monitor model accuracy and update systems when necessary. Artificial intelligence works best as an additional tool supporting experienced cybersecurity professionals.
Conclusion
Cybersecurity works by combining protective technologies, monitoring systems, and responsible practices to reduce digital threats. Firewalls, antivirus software, authentication, and encryption provide different layers of security. Network monitoring and incident response help identify and manage problems that bypass preventive controls. Understanding these processes makes the role of cybersecurity easier to recognize in everyday technology.
Individuals and businesses benefit from maintaining strong passwords, enabling multi-factor authentication, updating software, and protecting important information. Reliable backups and careful handling of suspicious messages provide additional safeguards. However, no single tool can guarantee complete security. Effective protection depends on using several appropriate measures and reviewing them as threats and technologies change.
Whether you are learning cybersecurity for personal knowledge or professional development, understanding practical examples is a useful starting point. Online banking, cloud storage, email filtering, and workplace networks demonstrate how security measures operate together. Building safe digital habits and learning how different protections work can reduce unnecessary risks. Cybersecurity remains an ongoing process that requires awareness, preparation, and continuous improvement.
FAQs
How does cybersecurity work in simple words?
Cybersecurity works by using protective tools and safe practices to prevent unauthorized access, detect suspicious activity, and respond to digital threats. Common examples include passwords, firewalls, encryption, and security monitoring.
What is a real-life example of cybersecurity?
Online banking is a common example. Banks use authentication, encrypted connections, transaction monitoring, and additional verification procedures to help protect financial information and identify potentially unauthorized activities.
What are the main tools used in cybersecurity?
Common cybersecurity tools include firewalls, antivirus software, password managers, encryption systems, vulnerability scanners, and security monitoring platforms. Each addresses different risks and contributes to broader digital protection.
How does cybersecurity prevent hackers?
Cybersecurity reduces opportunities for unauthorized access through authentication, secure configurations, software updates, and network protections. Monitoring and incident response help identify and contain suspicious activities that bypass preventive measures.
Why is cybersecurity important in everyday life?
Cybersecurity protects personal accounts, online payments, devices, and sensitive information from digital threats. Using secure passwords, updating software, and recognizing suspicious messages can help reduce the risk of scams and unauthorized access.