
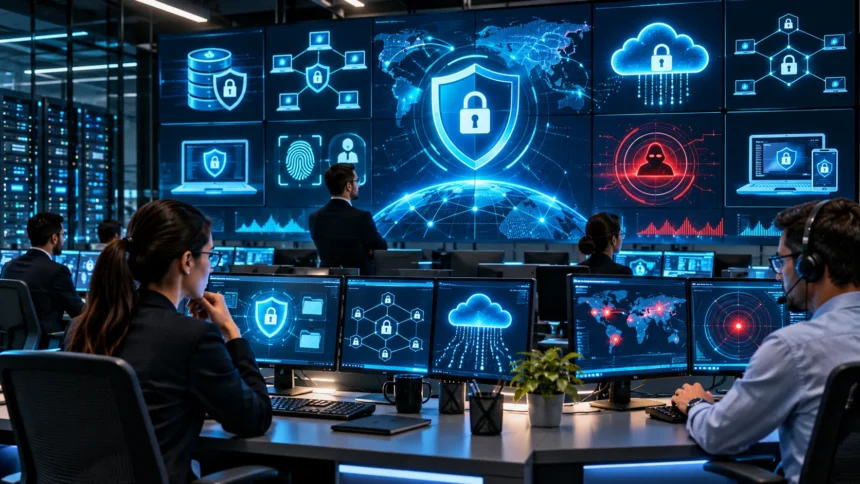
Cybersecurity plays an important role in protecting the digital systems people use every day. From online banking and healthcare platforms to business networks and cloud storage, modern technology depends on secure information systems. However, cyber threats such as phishing, malware, data breaches, and unauthorized access can affect individuals and organizations. Understanding cybersecurity applications helps explain how digital protection works in real-world environments.
Cybersecurity applications are tools, technologies, and security practices used to protect computers, networks, software, and sensitive information from cyber threats. They help organizations prevent attacks, detect suspicious activities, respond to incidents, and recover from security problems. This guide explains the major applications of cybersecurity, their practical uses, benefits, challenges, and importance across different industries.
What Are Cybersecurity Applications?
Cybersecurity applications are software tools, systems, and technologies designed to protect digital information and computer infrastructure. They help prevent unauthorized access, detect malicious activity, and reduce the impact of security incidents. Examples include antivirus software, firewalls, encryption tools, and intrusion detection systems. These security solutions support safer communication, data storage, and online activities.
The meaning of cybersecurity applications also includes the practical use of security technologies across different environments. Businesses use cybersecurity systems to protect customer information, while hospitals secure patient records and medical devices. Financial institutions apply security controls to online transactions and banking platforms. Each environment requires protection based on its specific risks and operational needs.
Cybersecurity applications usually work together rather than operating as independent solutions. A firewall may filter network traffic, while endpoint protection monitors activity on employee devices. Identity management systems control user access, and monitoring platforms identify unusual behavior. Combining these technologies creates multiple layers of protection that help organizations manage cybersecurity risks more effectively.
Why Are Cybersecurity Applications Important?
Cybersecurity applications are important because modern organizations depend heavily on digital information and connected technology. Business operations, financial transactions, communication systems, and customer services often rely on internet-connected platforms. Without appropriate safeguards, attackers may exploit security weaknesses to access information or interrupt operations. Effective cybersecurity measures help reduce these risks and support reliable digital services.
Protecting sensitive information is another major reason organizations invest in cybersecurity. Personal details, financial records, business documents, and confidential communications can be valuable targets for cybercriminals. Unauthorized disclosure may result in financial losses, privacy violations, and damaged customer relationships. Security applications help organizations protect information through access restrictions, encryption, monitoring, and other preventive controls.
Cybersecurity also supports business continuity and operational stability. A successful cyberattack can interrupt services, prevent employees from accessing systems, or damage important data. Organizations with strong security controls are better prepared to identify threats and restore affected operations. As a result, cybersecurity becomes an essential part of responsible technology management and long-term organizational planning.
Network Security Applications and Their Uses
Network security applications protect the communication systems that connect computers, servers, mobile devices, and other technology. These tools monitor network traffic and help prevent unauthorized access to digital resources. Common examples include firewalls, intrusion detection systems, and secure remote access solutions. Their primary purpose is to reduce threats affecting the confidentiality, integrity, and availability of network services.
Firewalls are among the most widely used network security technologies. They examine incoming and outgoing network traffic according to predefined security rules. Organizations can use firewalls to restrict unnecessary connections and separate sensitive systems from less trusted networks. Modern firewall platforms may also provide application awareness, traffic inspection, and additional threat prevention capabilities.
Intrusion detection and prevention systems provide another layer of network protection. These tools analyze network activity to identify suspicious traffic, known attack patterns, or unusual behavior. Some systems generate alerts, while others can automatically block certain malicious connections. When configured and maintained properly, these technologies help security teams recognize potential threats before they cause widespread disruption.
Endpoint Security Applications for Devices
Endpoint security focuses on protecting individual devices connected to an organization’s network. These devices may include desktop computers, laptops, smartphones, tablets, and company-managed workstations. Because employees frequently access sensitive information through endpoints, compromised devices can create significant security risks. Endpoint protection applications help identify malicious software, unauthorized activity, and potentially harmful system changes.
Antivirus and anti-malware programs are familiar examples of endpoint security applications. They scan files, applications, and system activity for known threats and suspicious behavior. Some products also provide real-time protection against malicious downloads and unsafe processes. Regular software updates help these applications recognize newly discovered threats and maintain stronger protection.
Endpoint detection and response solutions provide more advanced security monitoring and investigation capabilities. They collect relevant activity data, identify suspicious patterns, and help security teams investigate possible incidents. Depending on the product and configuration, they may isolate affected devices or stop harmful processes. These capabilities improve visibility across organizational devices and support faster incident response.
Cloud Security Applications and Data Protection
Cloud security applications protect information, software, and digital services hosted on cloud computing platforms. Organizations increasingly use cloud environments for file storage, collaboration, application hosting, and business operations. Although cloud providers offer security capabilities, customers still have responsibilities for protecting their configurations, identities, and information. Cloud security tools help address these responsibilities.
Cloud security posture management solutions identify potential configuration problems within cloud environments. They may detect unnecessarily public storage resources, excessive permissions, and settings that do not follow organizational security policies. These findings help administrators prioritize improvements before weaknesses are exploited. However, alerts require proper investigation because not every identified configuration creates the same level of risk.
Other cloud security applications focus on workload protection, identity management, and data security. Encryption can protect stored information and data moving between systems. Access controls limit which users and applications can interact with cloud resources. Together, these measures support safer cloud operations while helping organizations maintain visibility and control over their digital assets.
Application Security in Software Development
Application security involves protecting software against vulnerabilities that could expose information or allow unauthorized actions. Web applications, mobile apps, and business platforms may contain weaknesses introduced during design, development, or maintenance. Security applications help developers identify these problems before attackers exploit them. Effective protection requires attention throughout the software development lifecycle.
Static application security testing tools examine source code or related application components for potential security weaknesses. Dynamic testing evaluates running applications to identify certain problems in their behavior and exposed interfaces. Software composition analysis tools examine third-party dependencies for known vulnerabilities. Using these approaches together helps development teams identify different categories of software risk.
Secure development practices are equally important because scanning tools cannot identify every possible vulnerability. Developers should apply appropriate input validation, authentication controls, authorization checks, and secure coding standards. Regular security reviews and timely updates help address discovered weaknesses. Integrating these activities into development workflows reduces preventable risks while supporting dependable software delivery.
Identity and Access Management Applications
Identity and access management applications control who can access digital systems and what actions they can perform. Organizations use these tools to manage employee accounts, authentication processes, and access permissions. Without proper access controls, unauthorized users may reach confidential information or sensitive business functions. Identity management helps reduce these risks by establishing consistent access policies.
Multi-factor authentication is a common security measure supported by identity management systems. It requires users to verify their identity through more than one authentication factor, such as a password and a registered authentication device. This additional protection can reduce the risk associated with stolen passwords. However, authentication methods should be selected carefully because their resistance to phishing varies.
Role-based access control is another useful identity management approach. It assigns permissions according to job responsibilities rather than providing every employee with broad system access. For example, accounting employees may access financial records without receiving administrative control over unrelated systems. Regular permission reviews help organizations maintain appropriate access as employee responsibilities and business requirements change.
Data Security and Encryption Applications
Data security applications protect information against unauthorized disclosure, alteration, and loss. Businesses often store customer records, financial details, internal documents, and other sensitive information across multiple platforms. Protecting these assets requires appropriate controls throughout their lifecycle. Data classification, encryption, access restrictions, and backup systems all contribute to effective information security.
Encryption converts readable information into a protected form that requires appropriate cryptographic keys for authorized access. Organizations commonly use encryption to protect data stored on devices and information transmitted across networks. This reduces exposure when storage media are lost or communications are intercepted. However, encryption does not eliminate risks involving compromised accounts, insecure endpoints, or poorly managed keys.
Data loss prevention applications help organizations detect and control certain forms of sensitive information movement. These tools can identify protected content and apply policies when information is shared through email, cloud services, or other channels. Their effectiveness depends on accurate classification and carefully designed rules. Strong data protection combines technical controls with employee training and responsible information handling practices.
Cybersecurity Applications in Banking and Finance
Financial institutions use cybersecurity applications to protect online banking platforms, payment systems, and confidential customer information. Banks process large volumes of sensitive transactions, making security an essential operational requirement. Authentication systems, encryption technologies, and transaction monitoring tools help protect digital financial services. These measures reduce opportunities for unauthorized access and financial fraud.
Fraud detection applications analyze transaction activity to identify unusual patterns that may indicate unauthorized behavior. For example, a sudden change in account activity could trigger additional verification or a security review. Some systems use machine learning to identify patterns across large datasets. However, suspicious activity does not always indicate fraud, so careful investigation remains necessary.
Financial organizations also use cybersecurity tools to support regulatory compliance and operational resilience. Secure recordkeeping, controlled access, and incident monitoring help protect financial information. Regular security assessments can identify weaknesses in banking applications and supporting infrastructure. These safeguards support customer confidence while helping financial institutions maintain reliable digital services.
Cybersecurity Applications in Healthcare
Healthcare organizations use cybersecurity applications to protect patient information, hospital networks, and digital medical systems. Electronic health records contain confidential details that require careful handling and appropriate access restrictions. Security applications help healthcare providers control access and monitor suspicious activities. Protecting these systems supports patient privacy and dependable medical services.
Connected medical devices create additional cybersecurity considerations because they communicate with hospital networks and other systems. Security teams may monitor device communications, identify vulnerable software, and restrict unnecessary network connections. These measures reduce opportunities for unauthorized access and service disruption. Healthcare organizations must also coordinate security changes carefully to avoid interfering with essential medical functions.
Hospitals can strengthen cybersecurity through secure backups, employee training, and clearly documented incident response procedures. Staff awareness is particularly important because phishing messages and unauthorized access requests can target healthcare employees. Regular risk assessments help identify systems requiring stronger protection. Combining technical safeguards with effective procedures supports safer and more reliable healthcare operations.
Threat Detection and Incident Response Applications
Threat detection applications help organizations identify suspicious activities across networks, devices, and digital services. Security information and event management systems collect and analyze relevant security logs from different sources. These platforms can identify unusual patterns and generate alerts for further investigation. Centralized monitoring gives security teams better visibility into potentially harmful activity.
Security orchestration, automation, and response platforms help coordinate certain security operations. They can connect different security tools, organize incident information, and automate approved repetitive tasks. For example, a system might collect relevant alerts and prepare information for an analyst. Automation can improve efficiency, but important decisions still require appropriate oversight.
Incident response applications support organizations when cybersecurity problems occur. They help teams document events, investigate affected systems, coordinate recovery activities, and preserve relevant evidence. A structured response process can reduce confusion during an incident. Regular testing and improvements help organizations respond more effectively when unexpected security events threaten their operations.
Artificial Intelligence in Cybersecurity Applications
Artificial intelligence is increasingly used in cybersecurity applications to analyze large amounts of security information. Machine learning systems can identify patterns, compare activities, and highlight potentially unusual behavior. This can help analysts examine security events more efficiently. However, AI-generated findings should be evaluated carefully because automated systems can produce incorrect or incomplete results.
AI-assisted security platforms may support malware detection, phishing identification, and suspicious account activity monitoring. Some systems analyze behavioral patterns rather than relying exclusively on previously identified threats. This approach may help identify activity that differs from normal operations. Nevertheless, attackers can also adapt their techniques, making continuous evaluation of detection systems necessary.
Organizations should treat artificial intelligence as a supporting technology rather than a complete cybersecurity solution. AI systems require suitable data, careful configuration, and regular performance monitoring. Security professionals must also consider privacy, false alerts, and potential weaknesses in automated decisions. Combining AI capabilities with experienced human analysis helps create a more reliable security process.
Benefits and Challenges of Cybersecurity Applications
One major benefit of cybersecurity applications is their ability to reduce exposure to common digital threats. Security tools can help prevent unauthorized access, identify suspicious activity, and protect sensitive information. They also support more consistent security monitoring across organizational systems. When implemented effectively, these controls contribute to business continuity and stronger digital trust.
However, cybersecurity applications introduce financial, technical, and operational challenges. Organizations may need specialized employees, ongoing software maintenance, and investments in security infrastructure. Poorly configured tools can create unnecessary alerts or interfere with legitimate business activities. Selecting technology that matches actual organizational risks is more effective than installing numerous disconnected products.
Another challenge is the constantly changing nature of cyber threats and technology. New vulnerabilities, software updates, and business requirements can affect existing security arrangements. Organizations must regularly review their controls and adapt protection strategies when necessary. Effective cybersecurity depends on continuous improvement rather than purchasing security software once and assuming every problem is solved.
How to Choose the Right Cybersecurity Applications
Choosing suitable cybersecurity applications begins with understanding the systems and information that need protection. Organizations should identify critical assets, relevant threats, and existing security weaknesses. A risk assessment helps determine which controls are most important. This prevents unnecessary spending on tools that do not address meaningful security requirements.
Businesses should also evaluate compatibility, ease of management, and ongoing support before selecting security solutions. A product that integrates with existing infrastructure may be easier to operate consistently. Reliable updates, useful reporting, and appropriate access controls are important considerations. Organizations should also understand the total costs of licensing, implementation, maintenance, and employee training.
After implementing cybersecurity applications, businesses should regularly assess their effectiveness. Security testing, configuration reviews, and incident exercises can reveal gaps that require attention. Employees should understand their responsibilities and know how to report suspicious activity. Combining appropriate technology with clear policies and regular improvements helps build stronger cybersecurity protection.
Conclusion
Cybersecurity applications protect digital systems, networks, software, and sensitive information from a wide range of security threats. They include firewalls, endpoint protection, encryption tools, identity management systems, and security monitoring platforms. Each technology addresses particular risks and contributes to a broader defense strategy. Understanding their functions helps individuals and organizations make informed security decisions.
Different industries use cybersecurity applications according to their operational requirements and information security needs. Banks protect financial transactions, healthcare providers secure patient records, and businesses defend important digital resources. Cloud services and connected devices also require specialized protection. Selecting the right security measures depends on understanding potential threats and maintaining appropriate safeguards.
Effective cybersecurity requires more than installing security software. Organizations must combine reliable applications with employee awareness, secure configurations, regular updates, and tested response procedures. Continuous monitoring and improvement help security controls remain useful as technology evolves. A layered and risk-based approach provides a stronger foundation for protecting modern digital operations.
Frequently Asked Questions (FAQs)
What Are Cybersecurity Applications?
Cybersecurity applications are tools and technologies that protect computers, networks, software, and information against digital threats. Examples include antivirus programs, firewalls, encryption tools, and security monitoring systems.
What Are Five Common Applications of Cybersecurity?
Five common applications are network security, endpoint protection, cloud security, application security, and identity management. Each protects a different part of an organization’s digital environment against unauthorized access or other security risks.
Why Are Cybersecurity Applications Important for Businesses?
Cybersecurity applications help businesses protect sensitive information, prevent certain unauthorized activities, detect security incidents, and maintain operational continuity. They also support customer trust and responsible information management.
How Is Artificial Intelligence Used in Cybersecurity?
Artificial intelligence helps cybersecurity tools analyze security events, identify unusual behavior, and prioritize potential threats. Human oversight remains important because automated detection can produce false alerts or overlook certain risks.
What Is the Difference Between Cybersecurity and Network Security?
Cybersecurity protects digital systems, applications, devices, and information against security threats. Network security is a specific area of cybersecurity focused on protecting network infrastructure, communications, and connected resources.