
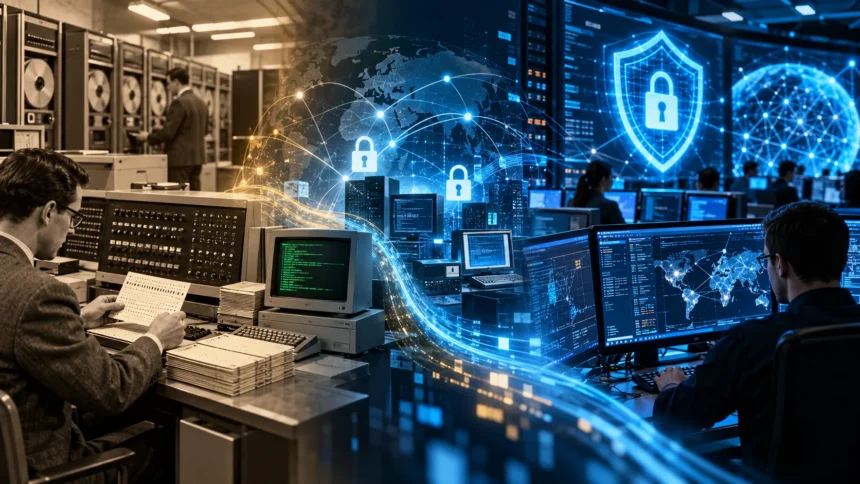
Cybersecurity has become an essential part of modern technology, protecting everything from personal information to critical business systems. However, the need to secure computers and digital information existed long before smartphones, social media, and modern internet services. Understanding the history of cybersecurity reveals how digital protection evolved alongside technological innovation.
The origins of modern cybersecurity can be traced to the 1960s and 1970s, when researchers began examining computer security and the risks associated with connected systems. Early developments such as ARPANET, the Creeper program, and the Reaper program helped demonstrate new security challenges. These discoveries gradually led to more sophisticated protection technologies.
Over the following decades, cybersecurity evolved from protecting individual computers into securing global networks, cloud platforms, and digital infrastructure. Today, it involves advanced technologies, professional security teams, international standards, and complex threat detection systems. This guide explores when cybersecurity began, how it developed, and the major events that shaped the industry.
What Is Cybersecurity and Why Did It Begin?
Cybersecurity is the practice of protecting computer systems, networks, applications, and digital information from unauthorized access, damage, disruption, and theft. It involves technologies, policies, and procedures designed to maintain information security. Although the term cybersecurity became widely recognized much later, the underlying need to protect digital information emerged during the early development of computers.
Early computers were primarily used by governments, universities, and research institutions. These machines often processed important scientific, military, or administrative information. As computer systems became more capable and accessible, organizations recognized the importance of controlling who could use them. Physical security, user permissions, and information protection became increasingly important.
The development of computer networking introduced additional security challenges because information could move between connected machines. Unauthorized users, programming mistakes, and malicious software created risks that extended beyond individual computers. Researchers began developing technical safeguards and security principles to address these problems. These early efforts gradually established the foundations of modern cybersecurity.
When Did Cybersecurity First Begin?
Cybersecurity does not have one universally accepted starting date because computer security developed through several overlapping discoveries. Its foundations emerged during the 1960s, when researchers studied access controls, computer reliability, and information protection. The field became more recognizable during the 1970s as computer networks expanded and dedicated security research programs appeared.
A major milestone occurred in 1969 with the establishment of ARPANET, an early packet-switched network that helped shape the modern internet. As more computers became connected, researchers gained opportunities to examine network behavior and security weaknesses. The growing ability to share information across systems created new questions about authorization, privacy, and protection.
In 1971, the experimental Creeper program demonstrated that software could move between connected computers. The development of Reaper soon afterward illustrated an early approach to removing such programs. These experiments are frequently mentioned in cybersecurity history. However, modern cybersecurity emerged through decades of research rather than a single invention or event.
Cybersecurity Before the Internet
Before modern computer networks became widespread, information security focused heavily on controlling physical access to computing equipment. Early mainframe computers were expensive machines located in universities, government facilities, and large organizations. Protecting them often involved restricted rooms, authorized personnel, and controlled access to storage media. These methods addressed the security requirements of centralized computing environments.
As multiple users began sharing computer systems, protecting information became more complicated. Organizations needed methods to distinguish authorized users and limit access to sensitive programs or files. Password systems, account permissions, and operating system protections gradually became more important. These developments introduced concepts that remain central to cybersecurity today.
Researchers also explored the relationship between computer security and privacy. Protecting information required more than securing physical equipment because users could access shared systems through terminals. Organizations increasingly considered how to prevent unauthorized disclosure or modification of data. These concerns helped establish computer security as a distinct area of technical research.
The Role of ARPANET in Cybersecurity History
ARPANET was an early computer networking project supported by the United States Advanced Research Projects Agency. Its initial network became operational in 1969 and connected research institutions through packet-switching technology. The project helped demonstrate how geographically separated computers could exchange information. These developments eventually contributed to the foundations of the modern internet.
ARPANET was designed primarily to support research and resource sharing rather than to provide comprehensive security against modern cyber threats. As the network developed, researchers encountered new challenges involving connected systems and user access. Information could travel between machines instead of remaining within isolated computing environments. This created additional opportunities for both technological innovation and security research.
The importance of ARPANET extends beyond its networking achievements. It provided an early environment in which researchers could observe the behavior of programs across connected computers. Experiments involving mobile software revealed possibilities that later became important to cybersecurity. The network’s development helped establish the relationship between connectivity and information security.
The Creeper Program: An Early Computer Worm
The Creeper program is one of the most frequently discussed milestones in the history of cybersecurity. Developed by computer researcher Bob Thomas around 1971, Creeper was an experimental program capable of moving between certain connected computers. It operated in an early networking environment and demonstrated a new form of software behavior.
Creeper is often described as the first computer virus, although historians commonly distinguish it from later viruses because of its worm-like characteristics. The program was created as a research experiment rather than as a modern criminal cyberattack. Its purpose was to explore whether software could move between systems. This distinction is important when interpreting its historical significance.
Creeper demonstrated that network-connected computers could be affected by programs originating elsewhere. Although the experiment was relatively limited, it raised questions about software control and system protection. The concept of programs traveling between computers later became central to understanding computer worms. Creeper remains an important example of early cybersecurity research.
Reaper: One of the First Antivirus Programs
Reaper is widely recognized as an early program designed to locate and remove the Creeper program. It is commonly associated with Ray Tomlinson and the early ARPANET research environment. Its development demonstrated that software could be created specifically to counter unwanted programs. This idea later became fundamental to antivirus and endpoint protection technologies.
Unlike modern antivirus applications, Reaper was not designed to detect thousands of malware families or continuously monitor personal computers. It addressed a particular experimental program within an early computing environment. Nevertheless, its purpose reflected an important security principle: software could identify and remove another program that was no longer wanted.
The historical importance of Reaper lies in its demonstration of automated software removal. Modern security products use much more advanced detection methods, including behavioral analysis and threat intelligence. However, the underlying objective of identifying harmful or unwanted software remains familiar. Reaper helped establish an early conceptual foundation for antivirus development.
Cybersecurity Development During the 1970s
The 1970s marked an important period in the development of computer security as a recognized technical discipline. Governments, universities, and technology organizations began studying how to protect increasingly complex computing environments. Research focused on access controls, authentication, system reliability, and information confidentiality. These developments extended beyond early experiments involving network programs.
In 1972, the United States National Bureau of Standards established a computer security program, representing an important institutional milestone. The organization later became the National Institute of Standards and Technology, commonly known as NIST. Its security work contributed to guidance and standards for protecting information systems. This helped formalize computer security practices.
Cryptographic research also advanced significantly during this decade. In 1976, Whitfield Diffie and Martin Hellman published influential work on public-key cryptography. The Data Encryption Standard became a United States federal standard in 1977. These developments helped establish encryption as an essential technology for protecting digital communications and information.
The Rise of Computer Viruses in the 1980s
During the 1980s, personal computers became increasingly common in businesses, educational institutions, and households. This expansion created new opportunities for software distribution and information sharing. It also introduced additional security challenges because malicious programs could affect systems outside specialized research environments. Computer viruses became a growing concern during this period.
One notable example was the Brain virus, which appeared in 1986 and affected IBM-compatible personal computers. It spread through infected floppy disks and became an important example of early personal computer malware. The incident illustrated how removable storage media could facilitate the spread of unwanted software. Similar threats encouraged greater attention to computer protection.
As malware incidents became more widely recognized, developers began producing antivirus programs for personal computers. Early security tools focused on identifying known malicious software through recognizable characteristics. These products were less sophisticated than modern endpoint security systems but represented important progress. The growth of personal computing helped establish antivirus software as a recognizable security category.
The Morris Worm and the 1988 Cybersecurity Turning Point
The Morris worm was released in November 1988 and became one of the most influential incidents in early internet security history. The program affected numerous Unix systems connected to the internet of that period. Its rapid spread disrupted normal computer operations and revealed weaknesses in networked environments. The incident attracted substantial attention from researchers and policymakers.
The Morris worm demonstrated how software could spread across interconnected systems and create widespread disruption. Although the internet was much smaller than it is today, the event highlighted important concerns about system vulnerabilities and network security. Organizations recognized that connected systems could experience problems extending beyond individual machines.
The incident also contributed to the development of more organized responses to computer security emergencies. In 1988, the Computer Emergency Response Team Coordination Center, commonly called CERT/CC, was established at Carnegie Mellon University. This represented a significant step toward coordinated incident response. Similar capabilities later became important components of cybersecurity programs around the world.
Cybersecurity in the 1990s: The Internet Revolution
The 1990s transformed cybersecurity as the internet became increasingly accessible to businesses and ordinary users. Websites, email services, and online communications introduced new ways to exchange information. Organizations began connecting internal computer systems to broader networks. This growth created security challenges that were more complex than those associated with isolated computers.
Malware, unauthorized system access, and insecure software became increasingly important concerns. Security technologies such as firewalls, antivirus programs, and network monitoring tools gained wider adoption. Businesses also began developing more formal information security policies. These measures helped organizations manage the risks associated with expanding internet connectivity.
The commercial growth of the World Wide Web increased the importance of protecting online information. Encryption technologies became essential for supporting secure communication and electronic transactions. Web browsers and online businesses required mechanisms for protecting transmitted data. By the end of the decade, cybersecurity was becoming an increasingly important business and technology responsibility.
The Development of Firewalls and Network Security
Firewalls emerged as important cybersecurity technologies as computer networks became more widespread. Their primary purpose is to control network traffic according to defined security rules. Early firewall technologies helped organizations manage communication between internal systems and external networks. This approach addressed the growing need to protect connected computing environments.
During the late 1980s and 1990s, firewall designs became more sophisticated. Different approaches included packet filtering, proxy-based controls, and stateful inspection. These technologies provided methods for evaluating network communication and restricting unwanted connections. Their development contributed to the growth of network security as a specialized discipline.
Modern firewalls continue serving important security functions, although their capabilities have expanded considerably. Contemporary network environments may include cloud services, remote connections, and complex application traffic. Security teams often combine firewalls with monitoring, authentication, and other protective technologies. Their history demonstrates how cybersecurity tools evolved alongside changes in network architecture.
The Growth of Antivirus Software
Antivirus software developed in response to the increasing spread of computer viruses and other malicious programs. Early products relied heavily on recognizable patterns associated with known threats. These tools helped identify suspicious files and protect personal computers from certain infections. Their importance increased as software sharing became more common.
During the 1990s and 2000s, antivirus products expanded their detection capabilities to address additional categories of malicious software. Vendors introduced more frequent updates and improved monitoring features. Security tools increasingly addressed worms, trojans, spyware, and other threats. These changes reflected the evolving nature of malicious software.
Modern endpoint security technologies use a combination of detection methods, including behavior monitoring and threat analysis. Traditional signature-based identification remains useful but is no longer the only approach. Organizations also integrate endpoint protection with broader security monitoring systems. The history of antivirus software illustrates the continuing relationship between emerging threats and defensive innovation.
Cybersecurity in the 2000s: The Growth of Digital Threats
The 2000s brought major changes to cybersecurity as businesses and consumers became increasingly dependent on the internet. Online banking, ecommerce, email communication, and digital services expanded rapidly. These developments created opportunities for innovation while increasing exposure to cyber threats. Protecting personal and financial information became a major security priority.
Phishing, spyware, computer worms, and online fraud became increasingly recognizable challenges. Attackers targeted individual users as well as business systems. Organizations needed stronger authentication, secure application development, and improved incident response procedures. Security awareness also became more important because many threats relied on deceiving users.
Cybersecurity gradually developed into a broader professional industry involving specialized teams, security vendors, and regulatory requirements. Businesses invested in monitoring systems, vulnerability management, and security policies. Governments introduced additional guidance and legal frameworks for protecting information. These developments helped establish cybersecurity as a central component of digital operations.
Major Cyberattacks That Changed Cybersecurity
Several high-profile cyber incidents influenced how organizations approach digital security. The Morris worm demonstrated the disruptive potential of networked malware during the 1980s. Later incidents revealed additional risks involving data theft, malicious software, and critical infrastructure. Each event contributed to greater awareness of the consequences of insecure technology.
The Stuxnet malware, discovered in 2010, became widely known for demonstrating the potential impact of malicious software on industrial systems. The WannaCry ransomware outbreak in 2017 disrupted organizations across multiple countries. Large data breaches also increased concerns about personal information protection. These incidents highlighted vulnerabilities extending beyond traditional office computers.
Major cyber incidents encouraged organizations to improve security planning, software maintenance, and incident response capabilities. They also demonstrated the importance of protecting operational technology and interconnected infrastructure. No single event created modern cybersecurity practices, but significant incidents repeatedly influenced priorities. Historical examples remain useful for understanding why security standards continue evolving.
The Rise of Cloud Security and Mobile Cybersecurity
Cloud computing transformed cybersecurity by moving applications, infrastructure, and information into remotely managed computing environments. Organizations increasingly adopted cloud services to support flexible operations and digital expansion. These changes introduced new responsibilities involving identity management, configuration security, and information protection. Traditional perimeter-based security approaches became less sufficient on their own.
The rapid adoption of smartphones also created additional security concerns. Mobile devices began storing financial information, personal communications, and access credentials. Security professionals developed methods to protect mobile applications, operating systems, and wireless communications. Device management and mobile authentication became important elements of modern security programs.
Cloud and mobile security required organizations to reconsider where information was stored and how users accessed it. Remote work further increased the importance of secure identity systems and protected connections. Cybersecurity expanded beyond protecting office networks to securing information across many environments. This transition helped shape the modern approach to digital security.
The History of Cybersecurity Standards and Frameworks
Cybersecurity standards developed as organizations recognized the need for consistent security practices. Early computer security guidance focused on protecting mainframe systems and controlling access to information. Over time, governments and professional organizations introduced more comprehensive standards. These frameworks helped businesses assess risks, define responsibilities, and improve security management.
One important milestone occurred in 2014 when NIST introduced the first version of its Cybersecurity Framework. The framework provided voluntary guidance for organizations seeking to manage cybersecurity risks. It emphasized identifying, protecting, detecting, responding to, and recovering from security incidents. These functions became widely recognized elements of structured security programs.
In February 2024, NIST released Cybersecurity Framework 2.0, expanding its scope and introducing stronger emphasis on governance. The updated framework recognizes cybersecurity as an organizational responsibility rather than only a technical activity. Its development reflects decades of progress in risk management. Modern standards continue adapting to changing technologies and business requirements.
Cybersecurity in the Age of Artificial Intelligence
Artificial intelligence has introduced new opportunities and challenges for cybersecurity. Security professionals increasingly use machine learning to analyze large volumes of information and identify unusual patterns. These tools can assist with monitoring, threat detection, and investigation. However, their effectiveness depends on the quality of data and the reliability of analytical models.
AI technologies also create new security risks involving model integrity, sensitive data, and automated systems. Organizations must consider how intelligent applications are developed, deployed, and protected. Security professionals increasingly collaborate with software engineers and AI specialists. This has contributed to the development of AI security as a growing technical specialization.
The relationship between cybersecurity and artificial intelligence continues evolving. Automated tools can reduce certain repetitive tasks, but human judgment remains essential for complex investigations and risk decisions. Security teams must also evaluate the limitations of AI-generated information. These developments represent another stage in cybersecurity’s ongoing technological transformation.
How Cybersecurity Has Changed Over Time
Cybersecurity began with relatively simple concerns about physical computer access and information protection. Early organizations relied on controlled facilities, user permissions, and basic system safeguards. As computers became connected through networks, security challenges expanded. Researchers developed new methods to address unauthorized activity and malicious software.
The growth of personal computers and the internet introduced additional risks affecting individuals and businesses. Antivirus programs, firewalls, encryption, and secure software practices became increasingly important. Later developments in cloud computing and mobile technology required broader security strategies. The field gradually evolved from isolated technical protections into coordinated organizational security programs.
Today, cybersecurity includes network security, application security, cloud protection, incident response, digital forensics, and risk management. Professionals work with advanced technologies while addressing both technical and human vulnerabilities. Although specific threats continue changing, the central objective remains consistent. Cybersecurity aims to protect information and maintain the reliability of digital systems.
Why Understanding Cybersecurity History Matters
Studying cybersecurity history helps explain why modern security technologies and practices exist. Many current protective measures developed in response to problems discovered during earlier periods of computing. Understanding those developments provides context for familiar concepts such as encryption, antivirus software, authentication, and incident response. It also reveals how security requirements changed over time.
Historical incidents demonstrate that security weaknesses can produce consequences beyond a single computer. Network worms, major data breaches, and infrastructure-related attacks highlighted the importance of coordinated protection. These events encouraged improvements in technical controls, professional training, and organizational planning. Learning from past incidents can support more informed security decisions.
Cybersecurity history also shows that technological innovation regularly creates new security challenges. The development of computer networks, personal devices, cloud services, and artificial intelligence each introduced additional risks. Understanding this pattern helps explain why cybersecurity requires continuous learning. Historical knowledge provides a useful foundation for students, professionals, and technology users.
Conclusion
The history of cybersecurity stretches back to the early development of computer systems and information security research. Although modern cybersecurity began taking shape during the 1960s and 1970s, its origins cannot be attributed to one person or invention. ARPANET, Creeper, Reaper, and early cryptographic developments helped establish important foundations for protecting digital information.
During the following decades, computer viruses, internet expansion, and major cyber incidents encouraged the development of antivirus software, firewalls, security standards, and professional response teams. Cloud computing, mobile technology, and artificial intelligence later introduced new security responsibilities. Cybersecurity evolved from protecting individual machines into securing interconnected digital environments.
Today, cybersecurity plays an essential role in protecting businesses, individuals, governments, and critical infrastructure. Its history demonstrates how security practices developed alongside technological progress. Understanding the major milestones provides valuable insight into modern digital threats and protective technologies. As computing continues evolving, cybersecurity will remain an important part of technological development.
Frequently Asked Questions
When Did Cybersecurity First Begin?
Modern cybersecurity began developing during the 1960s and 1970s as researchers explored computer access controls, network security, and information protection. Early experiments and dedicated research programs helped establish the field.
Who Is Considered the Father of Cybersecurity?
Bob Thomas is sometimes described as a pioneer of cybersecurity because he developed the experimental Creeper program in 1971. However, modern cybersecurity developed through contributions from many researchers rather than one individual.
What Was the First Computer Virus?
Creeper, developed around 1971, is often described as the first computer virus. More precisely, it was an experimental self-propagating program with worm-like behavior that demonstrated software movement across connected computers.
What Was the First Antivirus Program?
Reaper is widely recognized as one of the earliest antivirus-like programs. Developed in the early 1970s, it was designed to locate and remove the Creeper program from affected computer systems.
How Has Cybersecurity Changed Since the 1970s?
Cybersecurity evolved from basic computer access controls and early network experiments into a broad field covering malware protection, encryption, cloud security, incident response, and artificial intelligence security.